Review legal and compliance documents with clear source boundaries
PugID examines Legal / Compliance documents kept in Google Drive or SharePoint. A team member selects a legal-specific question. PugID identifies the relevant files and returns a structured result based on those documents. The legal or compliance team can then review the result against authoritative source documents and governed systems before putting it to use in a review or decision.
Bring legal evidence into one review
A legal or compliance review can rely on executed contracts, amendments, policies, regulatory calendars, matter trackers, incident records, data-processing agreements and control evidence. When these files reside across different folders, the reviewer must first confirm which version is executed, approved, current and within scope.
PugID operates at that document layer. It uses a chosen Legal / Compliance question to surface relevant material in connected Google Drive or SharePoint folders and produce a structured result. It does not replace contract lifecycle management, matter management, GRC, privacy, case-management or live reporting systems. Official records, legal interpretations, approvals and regulatory submissions stay in governed systems and with accountable professionals.
Choose the legal question you need to review
The supplied catalogue contains focused questions for contracts, obligations, policy, incidents, privacy and third-party risk.
Move from folders to a reviewable result
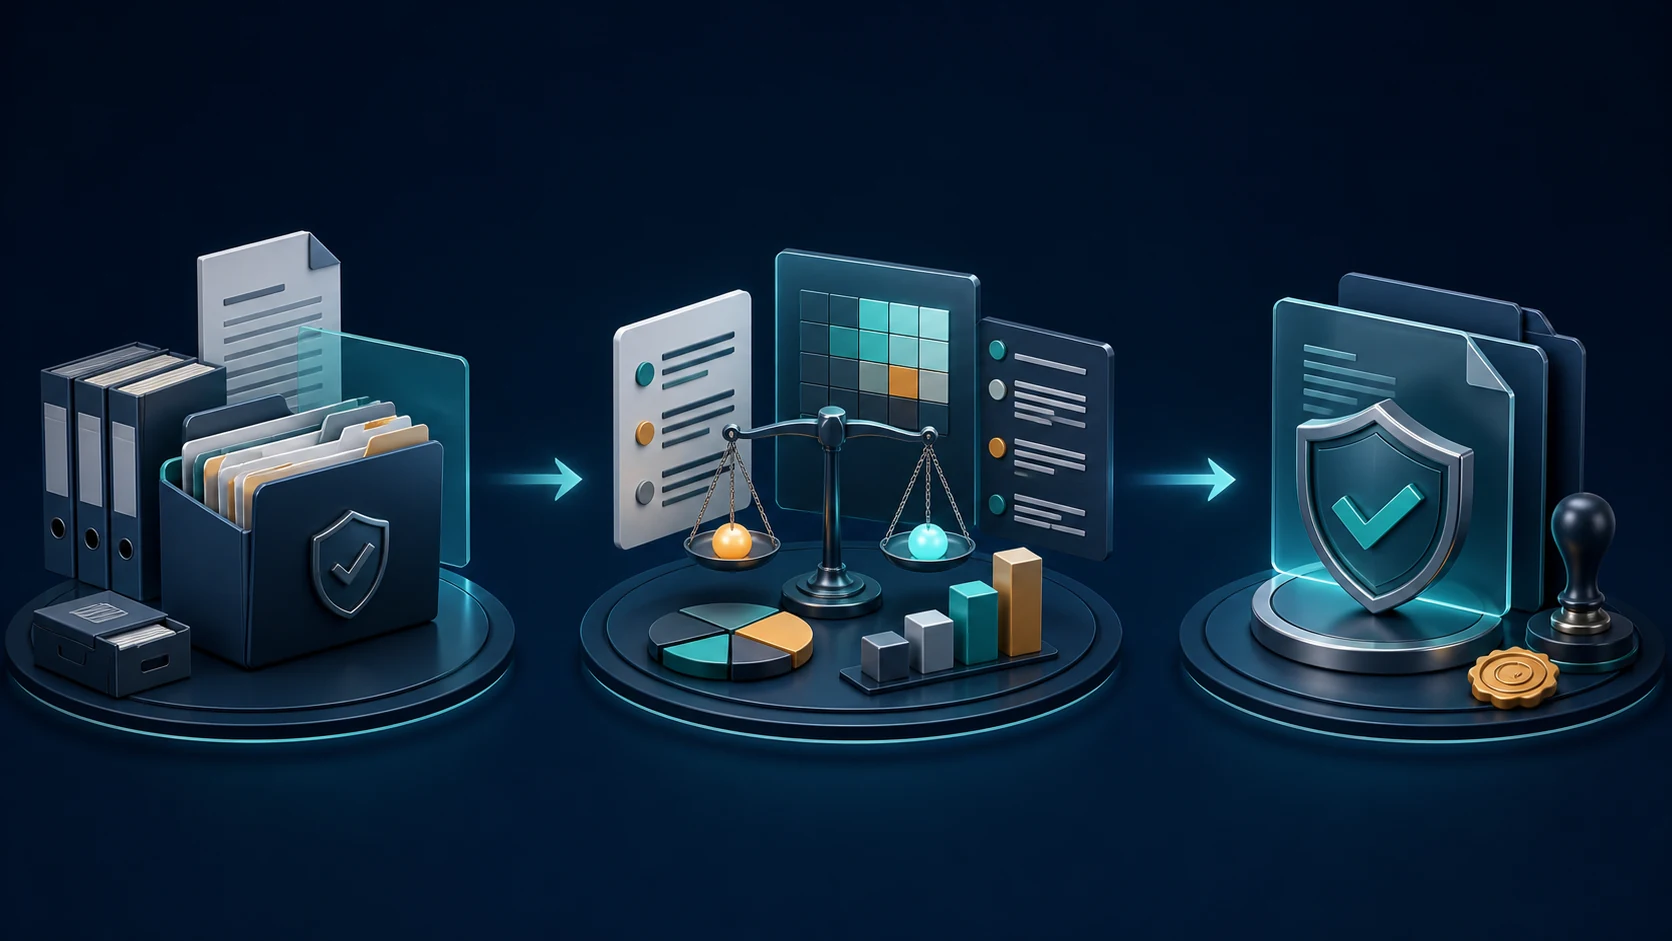
Connect approved folders.
Point PugID to the Google Drive or SharePoint locations that hold the documents relevant to the legal review.
Pick one Legal / Compliance question.
Select the prompt that matches the jurisdiction, matter, contract set or control review.
Review the structured result.
Check it against authoritative documents and governed registers, resolve conflicts and obtain professional approval before use.
Define the control model before testing
A controlled trial can gauge retrieval steps, document coverage, expired or conflicting items flagged, actions assigned and reviewer acceptance. Note the document set, jurisdictions, date range, confidentiality level, review owner and acceptance criteria before testing. These are suggested evaluation measures, not promised legal or compliance outcomes.
A clause can appear standard in isolation and shift meaning when an amendment, governing-law provision or related schedule is added. If two files conflict, examine execution status and source authority. A clean summary is only a map; counsel and compliance owners still determine which path is valid.
Keep controls, access and data handling in scope
PugID states that connections are encrypted, credentials are not stored, and documents and results are not kept permanently. It further states that temporary analysis data is removed automatically after eight hours.
Before connecting privileged, confidential, personal, investigation, hotline, sanctions or regulatory material, verify folder permissions, contractual terms, processing details, legal holds and internal policies. Rely on approved, minimised test data. Treat results as review material, not as legal advice, privilege determinations, regulatory submissions, sanctions decisions, formal approvals or evidence that an obligation has been discharged.