Review audit evidence with explicit source and accountability boundaries
PugID examines Internal Audit documents held in Google Drive or SharePoint. An auditor selects an audit-specific question. PugID locates the relevant files. It returns a structured result drawn from those documents. The audit team then verifies the result against approved audit files, evidence, control records and governed systems before using it in audit work or reporting.
Consolidate the audit question and evidence set in one review
An audit conclusion can rely on the approved plan, risk assessment, process narrative, control matrix, walkthrough notes, population file, sample selection, test sheet, supporting evidence, finding, management response and remediation record. Before reusing a status or exception, the reviewer must confirm the entity, process, control, period, population, sample, test step, evidence owner, version, review status and approval.
PugID operates at that document layer. It applies a chosen Internal Audit question to locate relevant material in connected Google Drive or SharePoint folders and deliver a structured result. It does not replace audit-management software, GRC platforms, SOX repositories, issue trackers, whistleblower systems, ERP records, identity systems, evidence archives or live business intelligence. Official workpapers, populations, samples, test results, findings, ratings, management responses, remediation decisions and reports stay in governed systems and with accountable auditors and control owners.
Select the audit question you need to review
The supplied catalogue contains targeted questions for audit plans, findings, remediation, SOX testing, policy compliance, walkthroughs, sampling and IT general controls.
Move from folders to a reviewable outcome
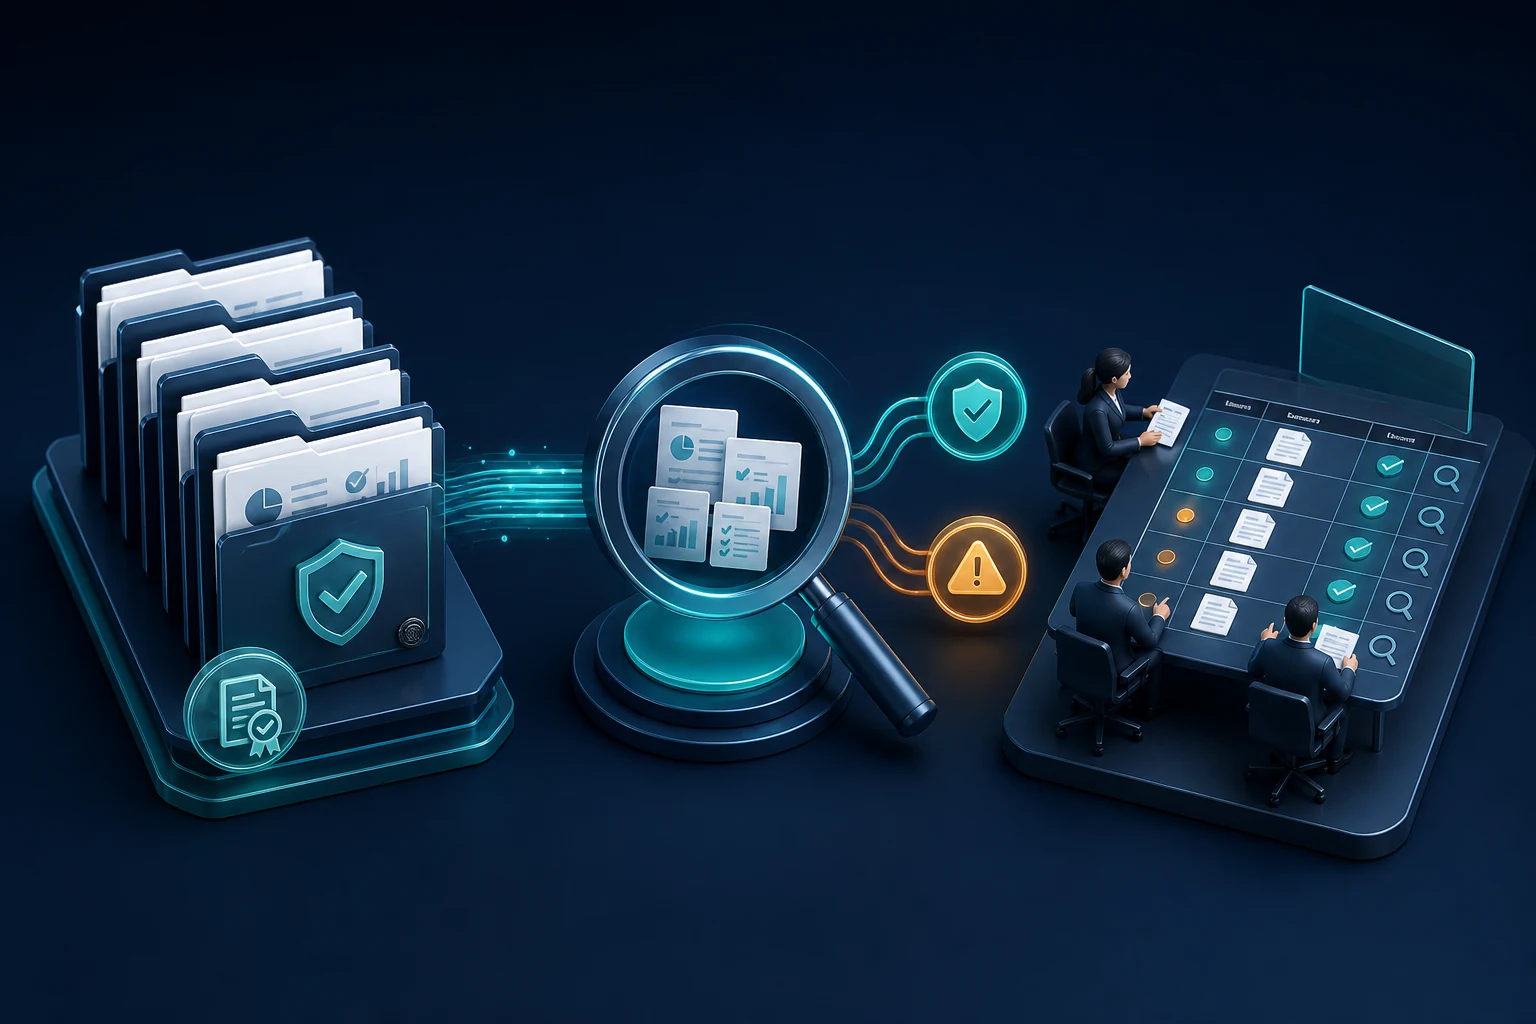
Connect approved folders.
Link only the Google Drive or SharePoint locations holding the audit documents relevant to the bounded review.
Select one Internal Audit question.
Pick the prompt that matches the entity, process, risk, control, period and approved evidence set.
Review the structured result.
Compare it with authoritative workpapers, populations, samples, systems and issue records; resolve conflicts and secure accountable audit review before use.
Maintain audit judgment, independence and evidence authority
PugID can organise information contained in documents. It does not design an audit plan, set materiality, pick a defensible sample, perform a control, verify evidence authenticity, determine control effectiveness, assign a final risk rating, close a finding, approve remediation, make a fraud determination or issue assurance. Auditors must assess relevance, reliability, sufficiency, completeness and contradictory evidence under the organisation’s methodology and applicable professional requirements.
A clean status can still rest on a stale population, missing evidence or management wording that has not been tested. Use the structured result as a review support. Retain professional scepticism, escalation and sign-off with the audit team, and maintain independence from management and control owners.
Set scope and acceptance criteria before testing
Document the audit, entity, process, risk, control, framework, period, population, sample, test step, evidence owner, evidence date, version, reviewer, issue status and acceptance criteria before a trial. Suggested measures include retrieval effort, source coverage, exceptions surfaced, conflicts found, reviewer acceptance and actions assigned. They are not commitments regarding assurance, control effectiveness, compliance, fraud detection, issue closure, risk reduction or return on investment.
Keep access, confidentiality and data handling within scope
PugID says that connections are encrypted, credentials are not stored, and documents and results are not kept permanently. It also says that temporary analysis data is removed automatically after eight hours.
Audit records may contain personal data, payroll and financial details, access records, allegations, whistleblower material, investigation content, security findings, legal advice, privileged material and evidence subject to retention or legal hold. Verify need-to-know permissions, confidentiality classification, segregation, personal-data controls, contractual limits, retention and legal-hold requirements before linking folders. Do not add passwords, keys, tokens or other secrets. Employ approved, minimised test data.
Run one bounded audit review
Start with a controlled task such as an open-findings summary, remediation-status review or audit-plan overview. Connect only approved folders, define the audit and authoritative evidence set, compare the result against governed workpapers and systems, and log every exception before broadening the evaluation.